Please wait
Loading
Preparing the page for you.
Please wait
Loading
Preparing the page for you.
Understand the core layers, components and technical decisions that shape a modern business application.
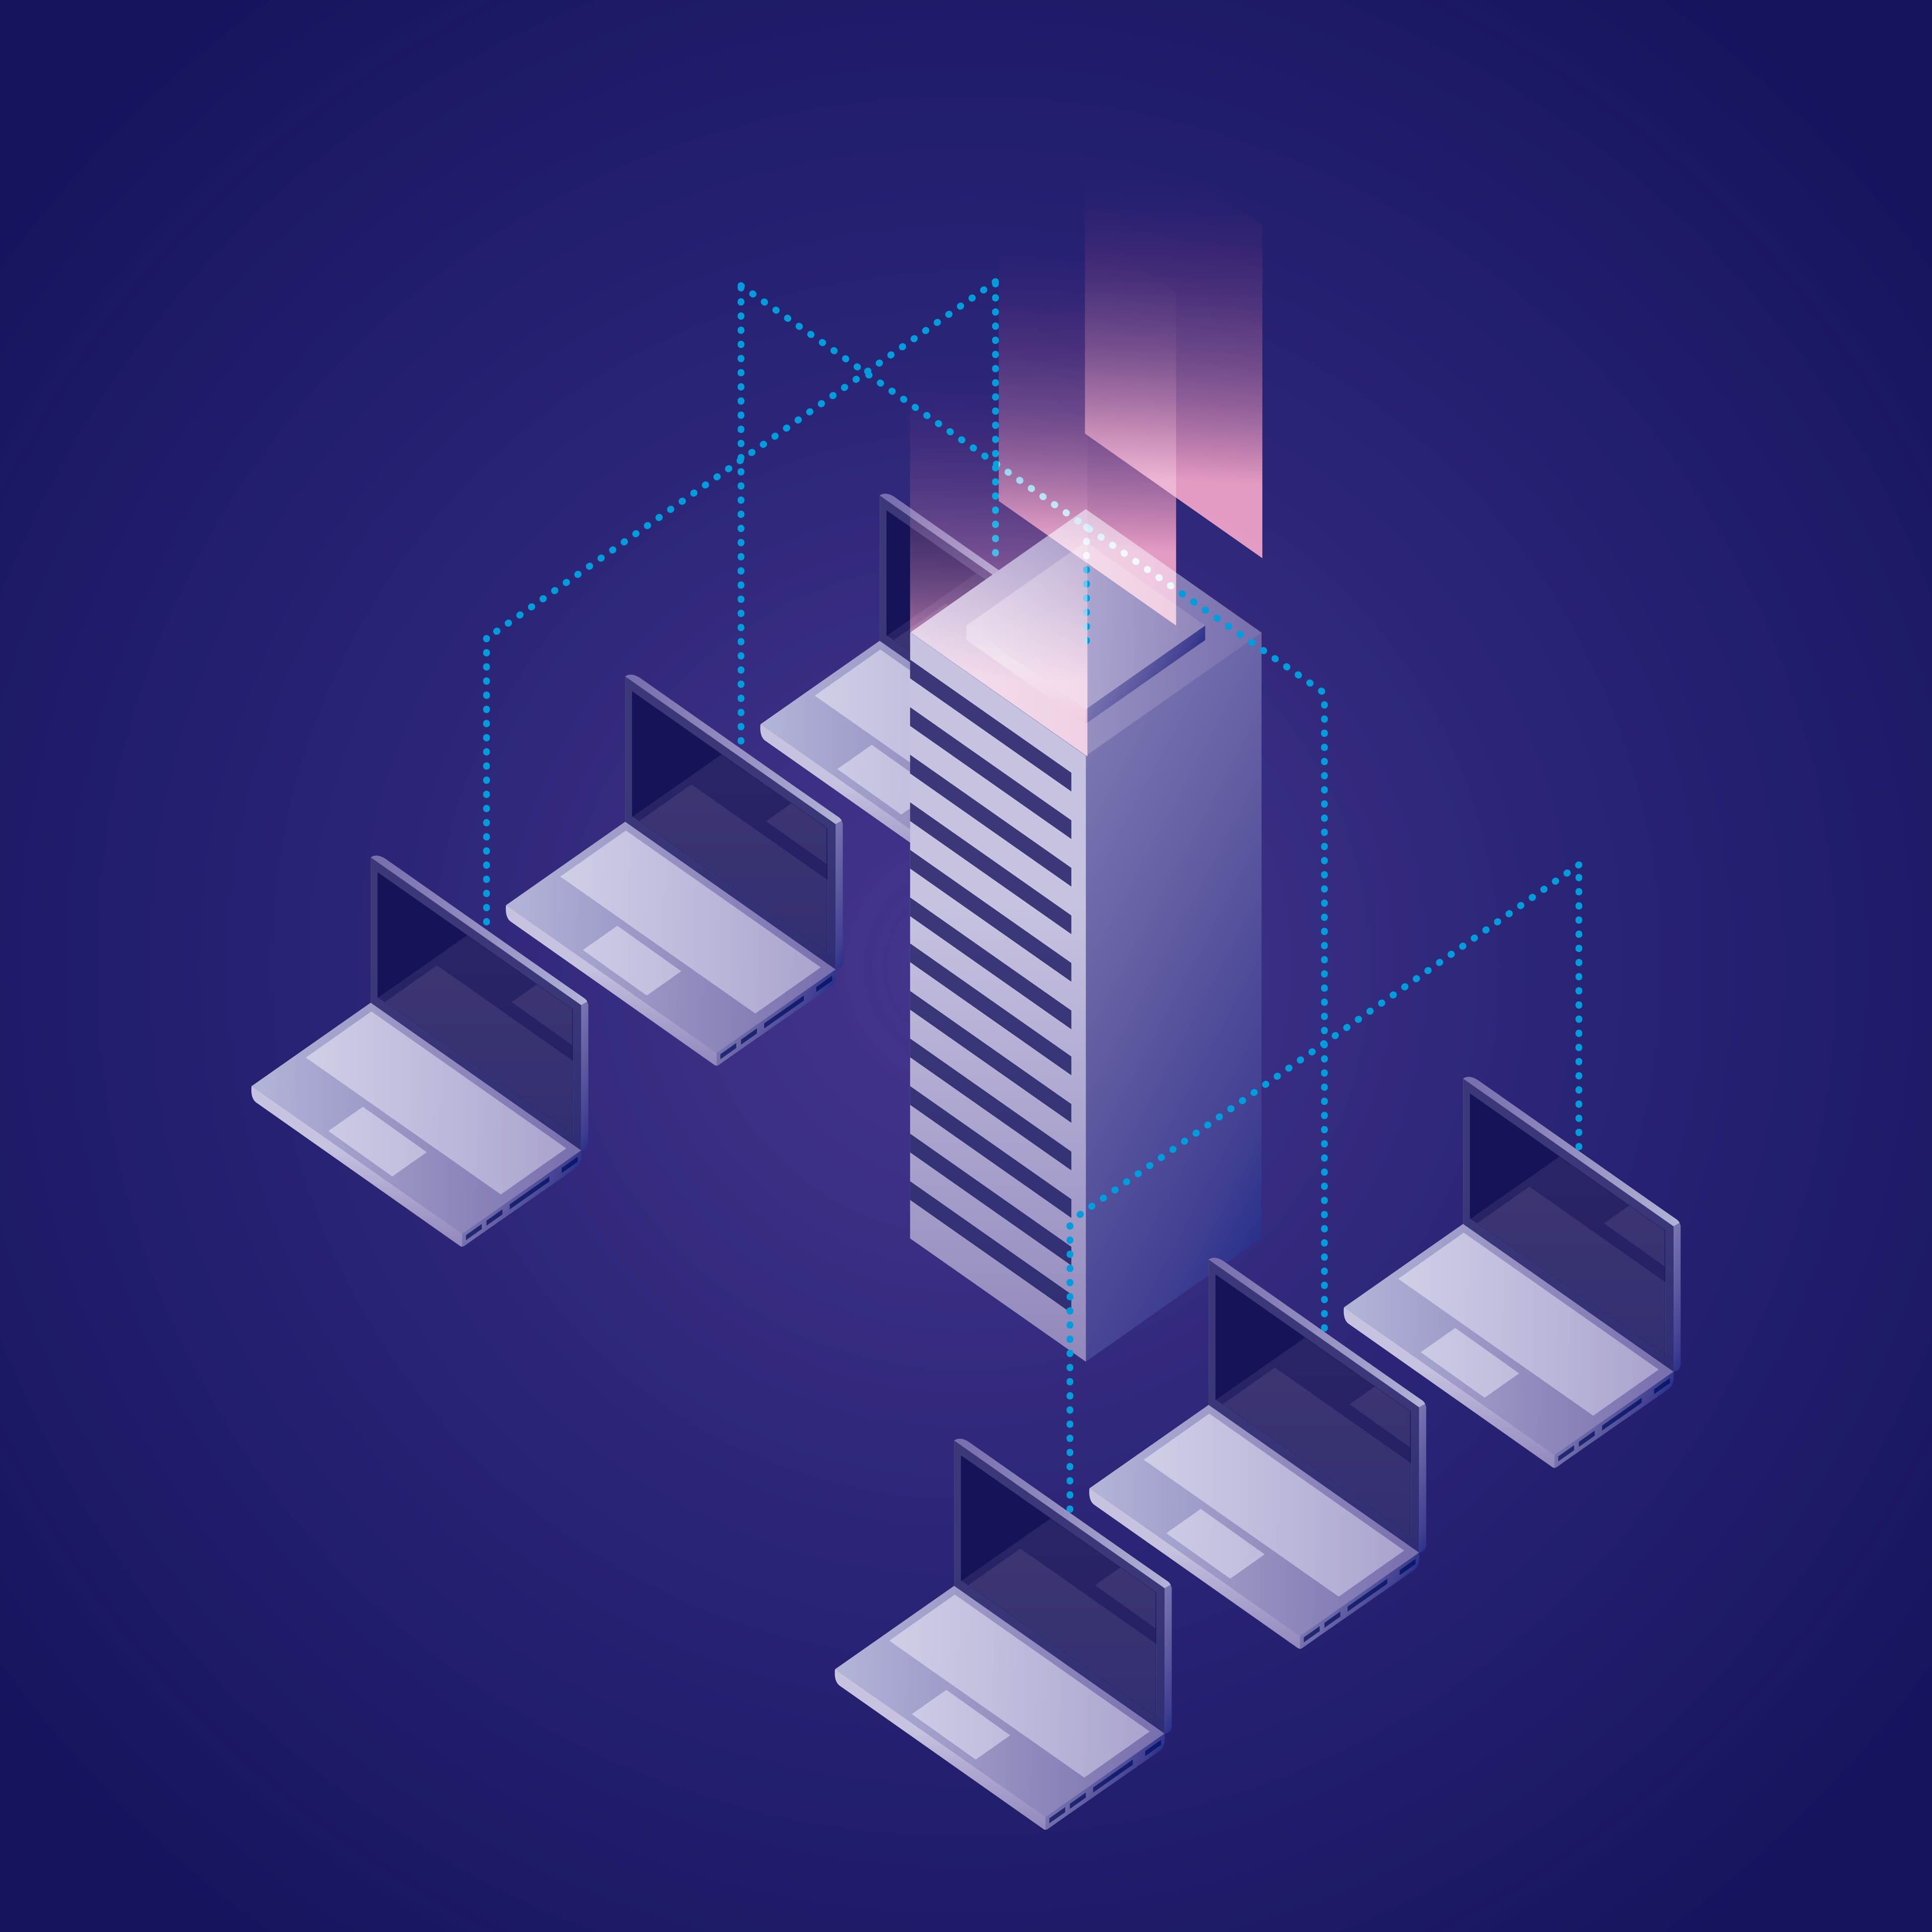
A business application is more than the screens employees or customers interact with. Behind every reliable application is an architecture that determines how the user interface, business rules, data, integrations, security and infrastructure work together.
Good architecture gives a business application a clear structure for growth. It helps teams introduce new capabilities without repeatedly rebuilding existing functionality, while also making the system easier to operate, secure and maintain. Poor architectural decisions can have the opposite effect: tightly coupled components, duplicated logic, fragile integrations and increasingly expensive changes.
There is no single architecture that is right for every organization. The appropriate approach depends on the application's purpose, users, data, integrations, expected scale, security requirements and long-term product strategy. The goal is to create an architecture that is appropriate for the business rather than adding technical complexity for its own sake.
Business application architecture is the structural design of a software system and the relationships between its major components. It defines how requests move through the application, where business rules are implemented, how information is stored, how external systems are connected and how the application is deployed and operated.
For example, a business application might provide a web interface for employees, an application layer that handles workflows and validation, a database for operational records, APIs for integrations and cloud infrastructure for running the system. These parts form a coordinated architecture rather than independent pieces of software.
The architecture should also establish clear boundaries. A user-interface concern should not contain critical business rules simply because doing so is convenient in the short term. Likewise, integration logic should not be scattered throughout unrelated features. Clear boundaries make future changes more predictable.
Many business applications can be understood through a layered architecture. The exact implementation may vary, but separating responsibilities into logical layers provides a useful foundation for design and maintenance.
These layers do not necessarily mean separate servers or separate applications. They are primarily boundaries of responsibility. In a well-designed system, the boundaries can remain clear even when several components are deployed together.
The presentation layer is the part of the application users see and interact with. It includes web interfaces, mobile interfaces, dashboards, forms, navigation and client-side behavior.
A strong architecture keeps the presentation layer focused on presenting information and collecting user input. Validation that is purely related to the interface can happen here, but important business rules should also be enforced on the server or in the appropriate domain layer so they cannot be bypassed by another client.
This separation becomes especially valuable when a business eventually introduces multiple channels. A web application, mobile application and internal API may all need to use the same underlying business capabilities without duplicating the rules in each interface.
The application and domain layers are where much of the business value of the system is expressed. They translate business requirements into workflows, decisions and rules that the software can execute consistently.
Consider an approval workflow. The application may receive a request, determine which workflow applies, check whether the requester has the required permissions, calculate the next approval step and record the resulting state. These decisions should have a clear home in the architecture rather than being spread across controllers, database queries and interface components.
Keeping business logic centralized also makes change easier. If an approval policy changes, the team should be able to update the relevant business rule without having to find and modify the same logic across several screens and integrations.
Business applications often depend on operational data that must remain accurate, consistent and accessible. Data architecture therefore needs to be considered alongside application architecture rather than treated as an implementation detail.
The design should establish which information the application owns, how entities relate to one another, which operations require transactions and how data is validated. It should also consider indexing, query patterns, backup and recovery, retention requirements and the expected growth of the data set.
Not every application needs a complex data architecture. A well-designed relational database can be an excellent foundation for many business systems. The important point is to choose the data model and persistence strategy based on actual requirements rather than following a technology trend.
Modern businesses rarely operate with a single software system. A business application may need to exchange information with CRM, ERP, accounting, payment, identity, logistics, analytics or third-party platforms.
An integration architecture defines how those systems communicate and where integration responsibilities belong. APIs are often used for synchronous interactions, while event-driven or asynchronous approaches can be useful when work does not need to complete within the original user request.
Good integration design also accounts for authentication, authorization, retries, timeouts, error handling, idempotency, logging and versioning. An integration that works in a happy-path demonstration but fails when an external system is unavailable is not a robust production integration.
Security should be part of the architecture from the beginning rather than added after development. Business applications frequently handle customer information, financial records, operational data or other information that requires controlled access.
Architecture decisions should cover authentication, authorization, session management, secrets, encryption, auditability and the principle of least privilege. Access should be based on clearly defined roles or permissions, and sensitive operations should be traceable where the business requires an audit trail.
Security also extends beyond the application code. Infrastructure configuration, deployment processes, dependency management, database access and third-party integrations all contribute to the application's overall security posture.
Scalability is often misunderstood as a reason to introduce distributed architecture immediately. In practice, many business applications can begin with a well-structured modular application and scale effectively as demand grows.
The better question is where the actual scaling pressure will occur. It might be database queries, file processing, API traffic, background jobs, reporting workloads or a specific high-volume feature. Architecture can then evolve around measurable requirements.
A modular monolith, for example, can provide strong internal boundaries while keeping deployment relatively simple. Services can be separated later when there is a clear operational or organizational reason to do so. This approach can reduce the cost of premature distribution while preserving a path for future evolution.
Architecture problems are not always caused by choosing the wrong technology. They often result from unclear boundaries and decisions that accumulate without a coherent structure.
The common thread is a lack of deliberate boundaries. A simpler architecture with clear responsibilities is often more maintainable than a technically sophisticated architecture whose responsibilities are difficult to understand.
Architecture should start with the business problem and the constraints around it. Before selecting frameworks, databases or infrastructure, define what the application needs to accomplish and what must remain reliable as it grows.
Answering these questions creates a practical architectural baseline. Technology choices can then be evaluated against that baseline instead of becoming the starting point for the entire design.
The strongest business application architectures balance structure with pragmatism. They create clear boundaries around business capabilities, keep critical logic in the right place, protect important data and provide reliable integration points without introducing unnecessary layers.
Architecture is also not a one-time diagram. As the application evolves, new requirements, integrations, workloads and security considerations will appear. Teams should periodically review architectural decisions and simplify areas that have accumulated unnecessary complexity.
For organizations investing in a custom business application, this means architecture should be treated as part of the product strategy. The objective is not to build the most elaborate technical system. It is to create a foundation that supports the organization's workflows today while providing a sensible path for tomorrow's requirements.
A modern business application should have an architecture that is understandable, secure, maintainable and capable of evolving with the organization. By establishing clear responsibilities between application layers, data, integrations and infrastructure, businesses can create software that is easier to change and operate over time. The right architecture is ultimately the one that supports the business effectively without adding complexity that the product does not need.
Explore the typical stages involved in taking a business application from requirements and design to development and launch.
Explore the technologies, platforms and development tools commonly used to build scalable business applications.
Learn what influences custom business application development costs in India and how project complexity affects the budget.